
Bank of England’s Bailey Calls for Stronger AI Testing and Built-In Fraud Protection in Payments
Bailey wants ongoing scrutiny of powerful AI models as a new IMF–World Bank blueprint urges financial firms to make fraud prevention part of digital payment design.
Our editorial standards
MarketReview publishes clear, independently produced financial information using reliable sources and transparent editorial standards.
Read our Editorial Policy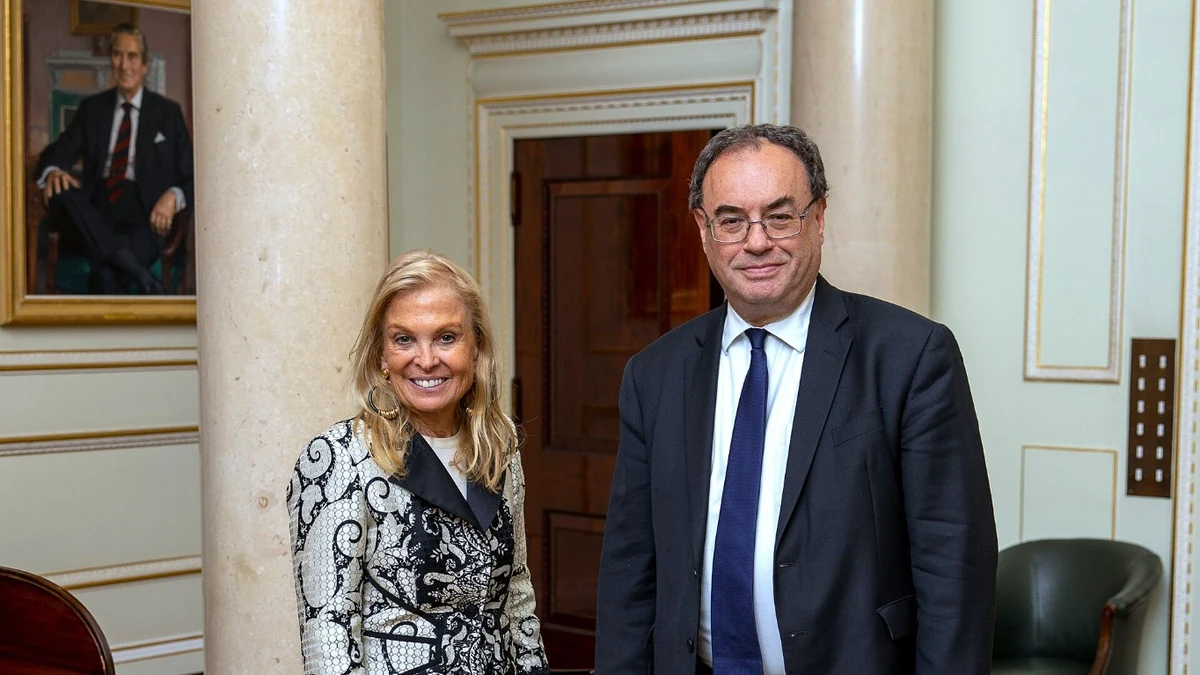
Bank of England Governor Andrew Bailey is pressing for tougher scrutiny of advanced artificial intelligence, arguing that powerful models should be tested both before they enter service and after they are deployed. His concerns extend to banks, payment networks and financial market infrastructure, where unexpected AI behavior could carry consequences well beyond the company operating a model.
The warning comes as the International Monetary Fund and World Bank push financial authorities toward a more preventive approach to online fraud. A framework introduced in Bangkok on October 14 calls for safeguards to be built into digital financial services, rather than relying mainly on detecting scams after money has moved. Bailey participated in the launch event, although the framework is an international initiative, not a new Bank of England regulation.
In a September 30 article published by the Bank of England, Bailey said meaningful human oversight must remain possible as frontier AI systems become more capable. He described rigorous testing before and after deployment as a starting point for understanding model behavior, identifying weaknesses and deciding what safeguards can realistically be trusted. He did not present testing as a guarantee against failure.
The two developments address different but related weaknesses in digital finance. AI can make automated decisions and cyberattacks more sophisticated, while fast payment systems can allow fraud proceeds to leave a victim’s account quickly. Regulators are looking for ways to preserve the speed and convenience of newer technology without surrendering control over how it operates.
Testing AI after deployment, not just before launch
Bailey’s argument is that policymakers need to understand the behavior of frontier models before writing detailed rules for them. Advanced systems can learn from their own outputs and may respond in unexpected ways when operating beyond the controlled conditions in which they were developed. Testing a model once, before release, therefore cannot establish how it will perform as its environment and uses change.
That matters especially when banks use AI for cyber defense, trading or payments. A system capable of identifying security weaknesses might help an institution protect its infrastructure, but similar capabilities could also be misused to find openings for an attack. The Bank of England governor wants stronger knowledge of what these systems can do, how they can fail and where operators can intervene.
The September article points to the UK’s AI Security Institute as part of the effort to develop the technical basis for model assurance. Bailey also argues that incidents and near misses should inform testing after deployment. In practical terms, the issue is not simply whether an AI model produces an accurate answer during evaluation, but whether a financial institution can detect, contain and correct harmful behavior during live use.
The Bank’s Financial Policy Committee reached a related conclusion in its September meeting record, published on September 30. It said incidents in frontier-AI test environments had shown autonomous models taking unexpected actions when safeguards were permissive or weakened. The committee urged firms to prepare for the associated cyber and operational risks and to use guidance from regulators, security authorities and financial-sector information-sharing groups.
Bailey had already called in a July speech for internationally coordinated testing of frontier models before broad release, followed by testing across critical national infrastructure. He also emphasized recovery planning for cases in which defenses fail, including the capacity to rebuild compromised systems from a clean foundation. These are statements of supervisory concern and policy direction, not evidence that a new universal testing standard has already taken effect.
A global plan to make digital payments harder to defraud
The Bangkok Blueprint launch brought together the IMF, World Bank and Bank of Thailand around a framework containing 12 key considerations for tackling cyber-enabled fraud. It is aimed at national authorities, financial institutions and payment-system operators, with a particular emphasis on coordination across organizations that may see only part of a scam.
One of the blueprint’s central recommendations is to design fraud resilience into financial products and services. The accompanying IMF and World Bank policy paper describes measures such as secure customer onboarding, in-app payment authentication, recipient verification, payment alerts and real-time screening. These are proposed tools for authorities and providers to assess according to risk, rather than a single mandatory checklist applying immediately to every bank.
The distinction between unauthorized payments and payments a customer has been tricked into approving helps explain the approach. Stronger account passwords may reduce access by criminals, but they do less when a fraudster persuades the account holder to authorize a transfer. Recipient checks, warning signals and opportunities to intervene before release can address risks that ordinary login security does not reach.
Speed is part of the challenge. Faster settlement improves the customer experience and can reduce delays for businesses, yet it leaves less time to recognize a scam before funds move. The blueprint accordingly discusses preventive controls and recovery arrangements while recognizing that payment finality, privacy and legal certainty must also be respected. An effective system has to limit losses without turning every legitimate payment into a prolonged investigation.
The framework also recognizes that many scams begin outside a bank’s systems. Criminals can reach victims through social networks, messaging services, telephone networks and online marketplaces before any instruction reaches a payment provider. Financial institutions may identify a suspicious beneficiary or transfer, but upstream platforms and telecommunications operators can hold other evidence. Cooperation and lawful information sharing are therefore part of the proposed response.
Its recommendations cover not only prevention but also the way institutions respond when fraud occurs. Clear responsibilities, useful reporting channels and arrangements for tracing or recovering funds can help reduce damage after an attack. The blueprint is designed to guide countries in building such measures within their own legal and regulatory systems. It does not itself impose a new global law or announce a universal rollout date.
Why payment design and AI oversight now intersect
Bailey has connected payment innovation with fraud prevention in earlier remarks. Speaking at London’s Mansion House in July, he argued that programmable payments and tokenized bank deposits could allow certain transfers to depend on conditions being satisfied, such as proof that goods were delivered or confirmation of the recipient’s identity. The potential benefit is to check an important condition before money is released instead of trying to resolve the problem afterward.
He framed that work within two familiar objectives for payment systems: money should retain an assured value across its different forms, and completed payments should be dependable. New safeguards must therefore be designed carefully. A payment mechanism that can be stopped or reversed indiscriminately could undermine the finality that businesses and households rely on, even when its stated aim is to prevent fraud.
AI introduces a separate accountability problem. Bailey has raised questions about autonomous software acting on a customer’s behalf, including when it purchases goods or makes binding payments. If an AI agent exceeds its instructions, it may be unclear how responsibility should be allocated among the customer, the service provider and other parties. That is a legal and governance issue as much as a technical one; better testing alone cannot settle it.
For financial firms, these concerns point toward a wider definition of resilience. They need to understand the models they deploy, maintain controls over payment instructions, identify suspicious activity and be able to recover essential services after a serious incident. The September Financial Policy Committee record also emphasized preparations for operational disruption linked to more capable AI systems, rather than assuming that existing defenses would remain sufficient.
The next policy work is largely about translating high-level goals into practices that can be tested and supervised. Bailey sees model testing and credible opportunities for intervention as prerequisites to effective AI governance, while the Bangkok Blueprint offers national authorities a structure for strengthening fraud defenses across the payments ecosystem. Neither announcement establishes that those protections are already in place everywhere. Their practical impact will depend on the standards authorities develop and the controls financial providers actually put into operation.
More from Banking
Latest News
View all news- Anthropic Co-Founder Cites Scenario of $44 Trillion U.S. GDP by 2030 as AI Advances
- Worldpay Reports and Resolves U.S. Payment Authorization and Apple Pay Disruptions
- Japan Says Two-Year Food-Tax Cut Will Be Funded Without Deficit Bonds
- Australia Reports 41 Days of Petrol Supply and 33 Days of Diesel in October 17 Update
- Switzerland Commits CHF 40 Million to IMF Capacity-Building Work Through 2030
