GAO Flags AI-Driven Cybersecurity Risks Across Financial Services and Critical Infrastructure
A federal technology assessment details faster AI-assisted attacks and new defensive tools, alongside 16 policy options for managing cybersecurity risks.
Our editorial standards
MarketReview publishes clear, independently produced financial information using reliable sources and transparent editorial standards.
Read our Editorial Policy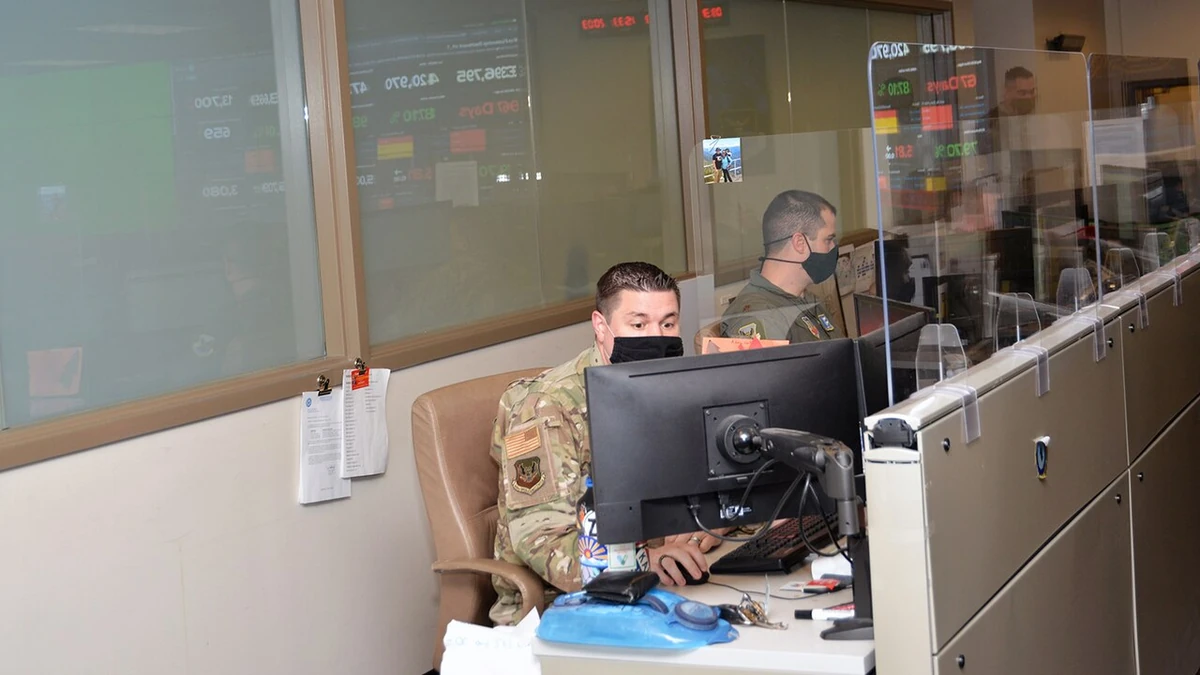
Artificial intelligence is making established cyberattack methods faster, more convincing and easier to scale, according to a new U.S. Government Accountability Office assessment that also documents growing use of AI to defend computer networks. The findings have implications for financial institutions and operators of essential services, where a compromised system can affect customers and operations well beyond the initial target.
The GAO technology assessment, published in November, examines AI-assisted attacks, defensive applications and the risks of putting increasingly autonomous software in charge of security functions. It identifies 16 policy options across four broad goals, but does not impose new cybersecurity rules or conclude that any particular industry has experienced a measurable rise in AI-caused breaches.
Financial systems appear alongside energy, water and telecommunications in the report’s discussion of critical services exposed to cyber threats. GAO’s central finding is broader than any one sector: the same technology that helps attackers find weaknesses and impersonate trusted people can help defenders detect suspicious activity and respond to threats before they spread.
AI is changing how quickly attacks can develop
Generative AI can produce realistic phishing messages, synthetic voices and other deceptive material at a scale that previously required more manual work. GAO says attackers can also use AI during reconnaissance, vulnerability discovery and attempts to evade security tools. These are extensions of familiar cybercrime techniques rather than proof that AI has created an entirely new class of attack.
The report highlights an emerging shift toward agentic AI, in which software agents can perform several stages of an attack with limited human direction. A malicious actor might use automated tools to investigate a target, adapt a technique and test whether a security product detects it. That possibility raises the importance of how quickly defenders can identify and contain activity after an initial compromise.
GAO cites an incident reported in February 2026 in which a relatively low-skilled attacker used commercial generative AI services in a widespread campaign involving stolen credentials. The attack also exploited weak passwords and the absence of multifactor authentication, according to the report. The example illustrates an important constraint on the AI narrative: existing security failures can remain the decisive opening even when attackers acquire more capable tools.
Another example in GAO’s review concerns a malware-testing operation reported in June 2026. Multiple AI agents were used to examine malicious code against different security products and look for ways to avoid detection. GAO presents these examples as part of its assessment of emerging practices, drawing on industry reporting rather than claiming that it independently investigated every underlying incident.
It is difficult to measure how prevalent AI-enabled attacks have become. GAO says there are no definitive technical indicators that reliably separate an AI-assisted intrusion from a conventional one. A rapid attack or unusually polished phishing message may suggest AI involvement, but those observations do not establish how the tools were used. The report therefore does not provide a sector-by-sector count of AI-driven cyber incidents.
Financial networks and essential services have different stakes
For banks and other financial businesses, the exposure includes unauthorized access, payment fraud, ransomware and interruptions to digital services. These are potential channels through which the wider threats described by GAO could affect the sector, not a list of specific new financial-sector incidents announced by the agency. A successful attack on a shared technology provider can also create operational concerns for more than one customer, depending on the systems involved.
The assessment gives examples of financial institutions using AI on the defensive side. One institution applied machine learning and language-processing techniques to identify probable phishing messages and reported fewer successful attempts against its customers. Another used automated analysis of normal user behavior to detect an active ransomware attack, helping it isolate affected systems before the malware spread. GAO attributes these examples to its review of existing literature and does not identify them as proof that all banks will obtain comparable results.
The appeal of these tools is the volume of information that security teams must process. AI can compare network behavior with established baselines, assess alerts, examine code for weaknesses and distill threat intelligence from multiple sources. It may give human analysts more time to investigate serious problems, although the quality of results depends on the data, the model and the controls around its use.
The consequences can be different in critical infrastructure. GAO discusses electricity-grid research into false data injection, in which manipulated sensor information could cause operators to make an incorrect decision. This is presented as a vulnerability scenario and area of defensive research, not as evidence that an AI-enabled attack disrupted a particular power grid. Similar questions about operational reliability arise wherever digital networks support physical services.
Greater use of AI in security also introduces new weaknesses. The report describes concerns about sensitive information being exposed to AI tools, uneven data quality and difficulties assessing what commercial products can actually do. Generative AI systems may produce inconsistent answers when given the same input, making performance testing and human oversight particularly important for decisions that affect live systems.
GAO also examines attacks aimed at AI agents themselves. When a tool reads an email, document or website that contains malicious instructions, it may treat that content as a command rather than untrusted information. Such an attack could redirect the agent toward an unintended action. The risk becomes more consequential as organizations move from using AI to summarize alerts toward allowing it to change configurations or take action on its own.
GAO outlines 16 policy options, not new mandates
The 16 options are organized around improving cybersecurity guidance, filling research gaps, governing AI tools throughout their use and maintaining workforce expertise. GAO describes them as alternatives that lawmakers, agencies, standards bodies and industry groups could consider. The assessment does not rank the options as a mandatory package or say that every suggestion should be adopted.
Several options address the possibility that a security team could become dependent on automated systems that later fail or behave unexpectedly. GAO discusses maintaining tested alternatives for critical functions, including rule-based software or manual processes. It also sets out the possibility of requiring human authorization before an AI system takes a consequential cybersecurity action, and of checking model output both before and after deployment.
Those proposals have practical implications for institutions with little tolerance for downtime. An AI tool may help a security center respond faster, but operators still need to know who can override it, whether its actions can be traced and how work will continue if the model becomes unavailable. In a regulated financial business or a utility, a successful pilot is not necessarily enough to establish that a tool is safe to use for high-impact decisions.
Other options include better information sharing, clearer approaches to AI-related privacy risks, more research on assigning identities and permissions to autonomous agents, and expanded testing environments. GAO also points to overlapping cybersecurity requirements as a challenge for organizations operating across sectors and jurisdictions. Efforts to reconcile those requirements would involve policymakers and regulators rather than taking effect automatically through this report.
Workforce skills are another area of concern. As automated tools take on alert review and routine analysis, specialists may have fewer opportunities to practice the manual techniques needed when systems malfunction. GAO includes options for retaining those skills alongside deeper AI expertise. The proposed approach recognizes that automation can increase capacity without eliminating the need for staff who understand its limitations.
More News
Latest News
View all news- FDIC Publishes Proposed Custodial Deposit Rules Affecting Smaller U.S. Banks
- India’s Forex Reserves Drop $14.2 Billion to $705.3 Billion, Lowest in Over Three Months
- Federal Reserve Releases New Survey of Banks’ Reserve-Management Strategies
- FirstEnergy Raises Five-Year Capital Investment Plan to $38 Billion
- MasTec Agrees to Acquire Murphy Corporation for About $1.25 Billion